Alpine Linux - CRITICAL - SSH bypass - Act now!
 AnthonySmith
AdministratorProviderOG

thanks to @nullnothere for the initial alert. https://lowendspirit.com/discussion/comment/245295/#Comment_245295
Links:
https://www.alpinelinux.org/posts/2026-11-05-openssh-password-authentication-bypass/
https://hachyderm.io/@damienmiller/117563026759098135
tl;dr people can log in to Alpine unless you already did specific additional actions.
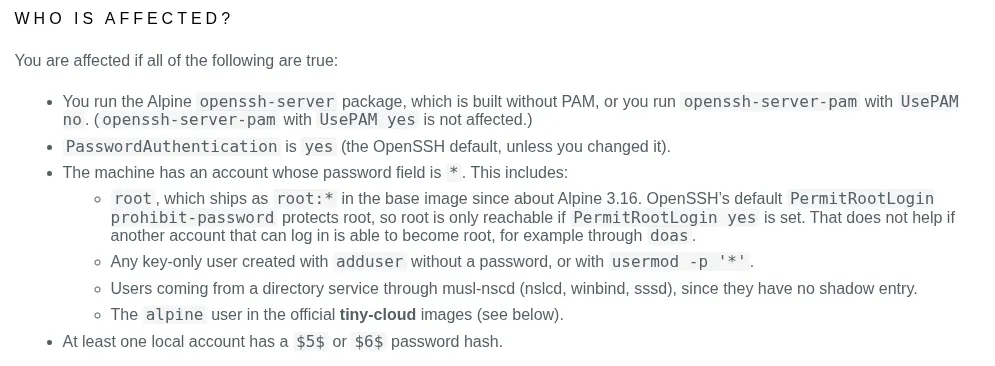
The problem is the default cloud images will be vulnerable, and its what almost everyone uses and anyone who spins their own likely did not think ahead and default options = vulnrable and it seems no one thought to remove the alpine user specifically as standard.
apk update && apk upgrade && reboot is probably best.
For TierHive people specifically (Other hosts please chime in and confirm your instructions), if you are running on very low ram please make sure the upgrade does not error/fail it is VERY easy to miss and if you reboot before the rebuild that will be the last reboot attempt you make as it will be dead, if it fails to update dont worry just add a temporary swap file to give you some headroom:
fallocate -l 128M /swapfiletemp && chmod 600 /swapfiletemp && mkswap /swapfiletemp && swapon /swapfiletemp && apk update && apk upgrade && swapoff /swapfiletemp && rm /swapfiletemp
Nasty one.
TierHive has updated the existing templates already, any older versions pinned to recipes have had first run commands added to apply some mitigations but they will now be removed in a few days so please update your recipes to use 3.23.8 or 3.24.4
TierHive - Hourly VPS - NAT Native - /24 per customer - DE, UK, SG, CA x2, USA x5, FR x3, AU, PL, NL, JP, BR, ZA
FREE tokens on sign up, try before you buy. | Static Hosting Free for life: https://tierhive.com/static-hosting/
Comments
emails sent to all users with an active VPS + Alpine installed with instructions, we will probably start to probe internally in 24 hours and shut down any VPS that is clearly vulnerable to avoid a shitstorm of abuse.
TierHive - Hourly VPS - NAT Native - /24 per customer - DE, UK, SG, CA x2, USA x5, FR x3, AU, PL, NL, JP, BR, ZA
FREE tokens on sign up, try before you buy. | Static Hosting Free for life: https://tierhive.com/static-hosting/
It is quite likely that there'll be some Docker related impact that will follow. I'm sure there are going to be some containers out there that do embed a vulnerable SSH setup in their Alpine images. If they're publicly accessible at all, they're all sitting ducks as well.
Yet another wake up call for those who refuse to embrace public keys and don't routinely use:
PasswordAuthentication no
AllowGroups somethinginclusive
If it helps your mental health, we get at LEAST 3 tickets per week asking what the username is.
TierHive - Hourly VPS - NAT Native - /24 per customer - DE, UK, SG, CA x2, USA x5, FR x3, AU, PL, NL, JP, BR, ZA
FREE tokens on sign up, try before you buy. | Static Hosting Free for life: https://tierhive.com/static-hosting/
Just confirmed the Void (musl) template is not vulnrable
TierHive - Hourly VPS - NAT Native - /24 per customer - DE, UK, SG, CA x2, USA x5, FR x3, AU, PL, NL, JP, BR, ZA
FREE tokens on sign up, try before you buy. | Static Hosting Free for life: https://tierhive.com/static-hosting/
Updated my TierHive alpine instances with the swap and had no issues. Thanks for the heads-up
Great.... another opportunity for botnets to expand... will this never end?!?
we've entered a new world, no way back...
I hope it ends soon, but I think we're in for a lot more vulnerabilities...
I have already applied the patch and restarted the system.
Although this issue does not affect me.