FBI seizes Virtualine.net (Omegatech LTD) hosting provider in "Operation OMEGALINE"
edited October 27 in General

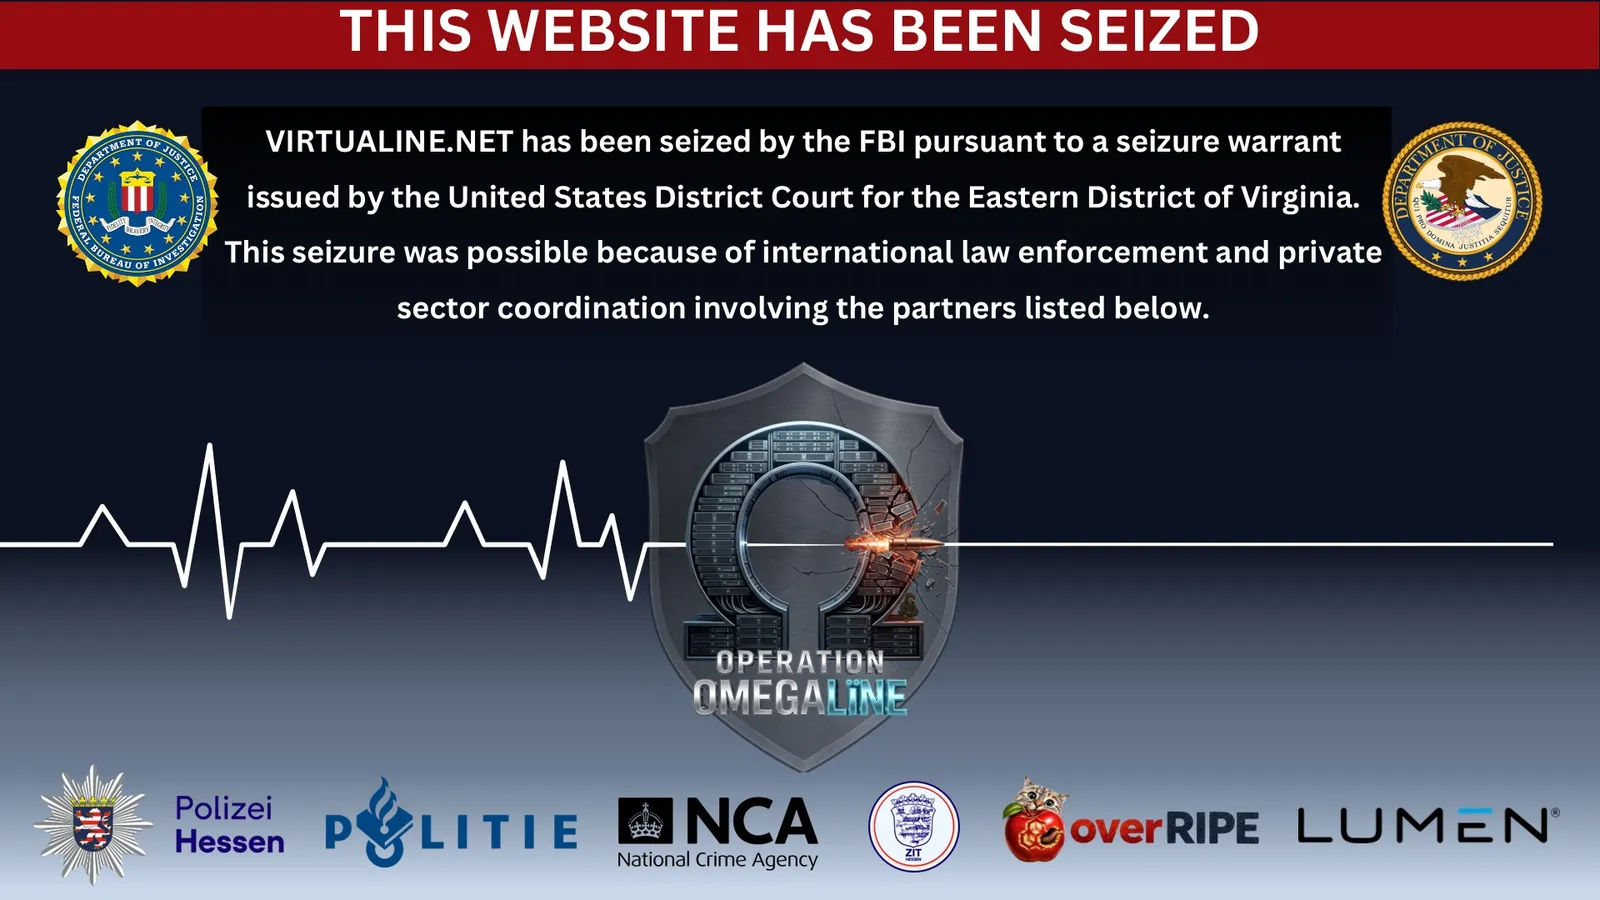
This morning FBI has put a seizure banner on a website of bulletproof hosting provider Virtualine.net (archive)
LowEndSpirit - VPS Hosting and tech forum

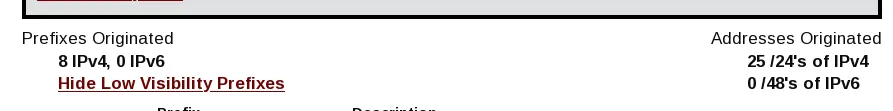
Virtualine operated primarily on AS202412 and AS219199 and as of right now, most of their subnets are gone. Only Pfcloud upstream remains. Aurologic was their primary upstream before, but I assume hardware at Tornado datacenter, was seized.
LowEndSpirit - VPS Hosting and tech forum

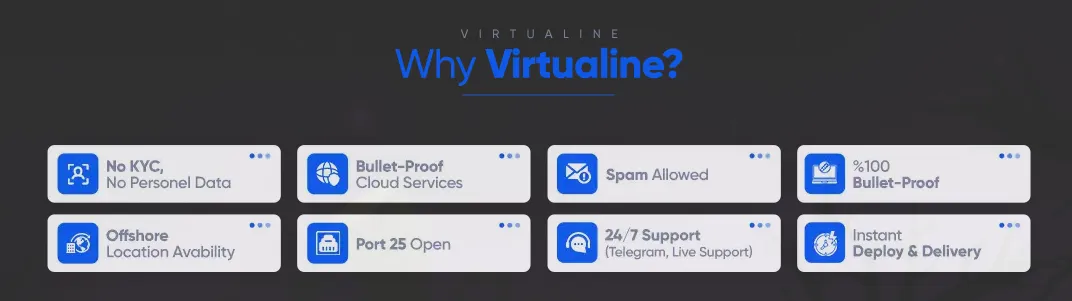
Their selling points were (that "Offshore" location was Germany):
LowEndSpirit - VPS Hosting and tech forum

Story is still developing, there are no news or press releases.

Comments

  • Aurologic, stories repeating.

  • girginosgirginos Provider

    He was probably providing services to IPTV providers.

  • edited October 27

    @girginos said:
    He was probably providing services to IPTV providers.

    He was primarily hosting phishing, malware and spam. Nothing to do with IPTV, he didn't even have capacity for it.
    It was your ordinary "bulletproof" host, like many using Aurologic.

    I have been aware of them for a few years now, they used to host in Turkey before but eventually moved over to Aurologic in Germany.

  • edited October 27

    @treesmokah said:

    @girginos said:
    He was probably providing services to IPTV providers.

    He was primarily hosting phishing, malware and spam. Nothing to do with IPTV, he didn't even have capacity for it.
    It was your ordinary "bulletproof" host, like many using Aurologic.

    I have been aware of them for a few years now, they used to host in Turkey before but eventually moved over to Aurologic in Germany.

    Could still be Turkey, I guess, tunneling via Aurologic? Also, what is OverRIPE?

  • OMEGALUL, who puts their "offshore" services in Frankfurt?

  • edited October 27

    @Gumbus said:

    @treesmokah said:

    @girginos said:
    He was probably providing services to IPTV providers.

    He was primarily hosting phishing, malware and spam. Nothing to do with IPTV, he didn't even have capacity for it.
    It was your ordinary "bulletproof" host, like many using Aurologic.

    I have been aware of them for a few years now, they used to host in Turkey before but eventually moved over to Aurologic in Germany.

    Could still be Turkey, I guess, tunneling via Aurologic? Also, what is OverRIPE?

    Its possible, I honestly don't remember when was the last time I checked their actual location. They had Aurologic GRE at the very least.
    I found a fairly recent traceroute to one of their IP's from RIPE Atlas, and it looks like its a remote DDoS protection tunnel from Aurologic. ~50ms to hop in Germany, so its tunneled to somewhere far away.
    https://atlas.ripe.net/measurements/224650252/results

    Anchor ID: 7724
    Source IP: 80.239.216.219
    🇸🇪 AS1299
    Min RTT: 53.42ms
    Responded: yes
    Complete Traceroute:
    Hop  IP Address  Hostname    ASN RTT (ms)
    1    80.239.216.217  ffm-b5-link.ip.twelve99.net     0.44/0.45/0.4
    2    62.115.136.212  ffm-bb1-link.ip.twelve99.net        17.93/17.65/17.78
    3    62.115.137.77   ffm-b23-link.ip.twelve99.net        2.56/2.09/2.25
    4    45.138.175.173  core01.fra3.de.aurologic.net        0.9/0.62/0.69
    5    45.138.175.172  core02.fra1.de.aurologic.net        0.89/0.82/0.92
    6    45.138.175.196  services-leaf01.any.aurologic.net       1.04/0.94/0.85
    7    45.138.175.206  remote.ddosprotection.io        1/54.9/1.07
    8    *   *   *   *
    9    94.26.38.21 russagromaslo.com       53.58/53.42/53.63
    

    They have also put out their own statement on one of the domains they own https://virtualine.org/ (archive)
    By what they are saying, it seems like the seizure was over them hosting CSAM. And from the looks of it, the operator has not been arrested (yet).

    OPEN LETTER · OCTOBER 2026

    To the law enforcement authorities,

    Dear officers of the FBI, Polizei Hessen, Politie Midden-Nederland, and the United Kingdom’s National Crime Agency,
    Perhaps you expected to see our operations resume here. Perhaps you expected a new website, an announcement about our services, or a response focused on the seizure of our domain.
    Yes, I could have done that. I still could. Perhaps it would take a day, perhaps even less. You know that as well as I do. I could rebrand, build a new website, and carry on.
    But that is not what I chose to do tonight. Perhaps this is the first time you have seen an open letter like this from a bulletproof hosting provider. I am not writing to make a point about the industry. I am writing because, before anything else, I am a human being, and I have moral principles that matter more to me than a domain or a business.
    Instead, I am writing this open letter. Because if I did not say these words tonight, I would not be able to sleep peacefully.
    Before I am the person behind Virtualine, I am a human being.
    I understand that Virtualine’s business model has attracted scrutiny. I understand that there are serious allegations concerning our services, our customers, and our finances. Those matters deserve a fair investigation, and we will address them through the proper legal channels.
    But reading the allegation that we knowingly hosted child sexual abuse material has affected me in a way I cannot simply set aside.
    I regard the sexual exploitation of children as a crime against humanity in the moral sense of those words. I cannot remain silent when I am accused of knowingly enabling something I find so profoundly inhuman.
    For five years, we have told our customers that CSAM is prohibited, without exception. This was not a rule invented after the seizure. It was part of our publicly stated policy, even in advertisements for services that others rightly regard as controversial.
    We have never refused a request for cooperation concerning CSAM, nor have we knowingly remained silent when such material was reported to us. To the best of our records and understanding, we took action on reports of this nature within 24 hours. When we identified prohibited material associated with the customer described as “Vendor 1,” we ended our relationship with that customer.
    I know that these statements must be examined against records, dates, and evidence. I am not asking anyone to accept them merely because I have written them.
    But I am asking you to look carefully at the full chronology: what was reported to us, when we received it, what action we took, and when the relevant services were terminated.
    For God's sake, you have seen the millions involved. Why would I knowingly put everything at risk over CSAM, especially in 2026, when Virtualine's business was going well? I understand that this question does not prove anything by itself. But it is a question I sincerely ask you to consider alongside the evidence.
    Virtualine has been part of my life for five years. A domain can be seized. A business can be investigated. Our decisions can be questioned. I accept that none of us is above the law.
    What is difficult to accept is being described as someone who knowingly facilitated the exploitation of children, when I believe the actions we took tell a different story.
    I also want to be clear: this letter is not an attempt to minimize the suffering of victims or to shift attention away from them. Their protection matters far more than the reputation of any hosting company.
    A personal request
    To Theophani K. Stamos, First Assistant U.S. Attorney for the Eastern District of Virginia, and Darren B. Cox, Assistant Director in Charge of the FBI Washington Field Office: I ask you, respectfully, to review the complete record and the steps we took in response to the reports concerning Vendor 1.
    To the officers and investigators involved in this operation: I respect the importance of your work in protecting victims. I ask only that our actions be assessed with the same care and seriousness as the allegations against us.
    We remain willing to provide relevant information through lawful channels and to address the allegations in the appropriate proceedings.
    I am not writing tonight because I am angry. I am writing because I am deeply hurt by this particular accusation, and because staying silent would feel like accepting something I do not believe to be true.
    Please be fair. Please examine the dates, the notices, and our responses. If you genuinely wish to learn more about “Vendor 1”. Please do not cast suspicion on me and the tens of thousands of customers who have trusted Virtualine because of the actions attributed to a single customer. I want you to know that I am prepared to respond to your requests concerning “Vendor 1”.

    With respect,
    VIRTUALINE
    The Fine Line of Privacy


    And here is the FBI new press release on this seizure: https://www.justice.gov/usao-edva/pr/bulletproof-website-domain-seized-international-law-enforcement-operation (archive)
    They do indeed mention serious CSAM hosting allegations and even direct cooperation with pedophiles.

    “Bulletproof” website domain seized in international law enforcement operation
    Tuesday, October 27, 2026
    For Immediate Release
    U.S. Attorney's Office, Eastern District of Virginia

    ALEXANDRIA, Va. – Theophani K. Stamos, First Assistant U.S. Attorney for the Eastern District of Virginia, and Darren B. Cox, Assistant Director in Charge of the FBI Washington Field Office, announced today the seizure of the website virtualine.net after it was used to commit and facilitate prolific criminal activity, including the advertisement of sexually explicit images of minors, the intentional disclosure of nonconsensual intimate visual depictions of adults and minors, and international money laundering designed to conceal and promote criminal conduct.

    According to court records, the United States obtained court authorization to seize virtualine.net, which is the website for Virtualine, aka Secury, Massgod, Spamhouse, Lanedo, and Omegatech. Virtualine is a “bulletproof” service offering hosting and server solutions with domain name purchasing options. Virtualine advertises its services to criminals on cybercrime forums. For example, in September 2024, Virtualine told a user on Exploit.in: “You can use Virtualine for all illegal/black hat activities (including phis[h]ing, carding, email spam, port scanning and all others) except for child contents and terrorism activities.” In March 2026, Virtualine advertised its “additional protection plan,” which it offered to its customers after “receiv[ing] an official request from law enforcement agencies.” Under this plan, Virtualine would move the customer’s criminal infrastructure to “another shell company not affiliated with Virtualine, after which the server is reactivated.” As Virtualine advertised to users on the platform HackForums in June 2025, “Virtualine ignored more abuse than your last three therapists.”

    Despite advertising that it does not allow “child contents” on its server, Virtualine knowingly hosted a website that did so, identified in court records as Vendor 1. Vendor 1 is a criminal online forum that allows users to post and sell access to nude, sexually suggestive, and/or sexually explicit images and videos of minors and adults. Vendor 1 also promotes a hack-for-hire service in which users can pay hackers to access victims’ online accounts without their consent and illicitly obtain explicit images and videos. In January 2026, about one month after Virtualine assigned an IP address to Vendor 1, Virtualine began receiving notifications about sexually explicit images and videos of minors on that server. Despite receiving numerous notices from law enforcement in Germany, Canada, and Australia; the National Center for Missing and Exploited Children (NCMEC) in the United States; and even from a victim’s attorney, Virtualine continued to host Vendor 1’s services. Furthermore, Virtualine worked closely with Vendor 1 to create a new website where Vendor 1’s clients could upload their illicit content and from which they downloaded it when they made a purchase. Virtualine hosts this new website to this day, and it has already received at least one abuse complaint about sexually explicit images of children found on that website.

    Virtualine.net included a number of payment options for Virtualine’s customers, including Vendor 1. Virtualine accepted payment through BTC [NO-AML], specific unhosted bitcoin addresses that allowed customers to direct pay without concern their funds would be flagged as illicit. The funds Virtualine’s criminal customers paid to Virtualine, some of which can be traced directly to various criminal groups, were received by Virtualine and then further laundered to conceal the origin of the funds.

    This case was investigated by the FBI Washington Field Office with significant assistance from Germany’s Polizei Hessen, the Netherlands’ Politie Midden-Nederland, the U.K.’s National Crime Agency, and private sector partners OverRIPE and Lumen. The Justice Department’s Office of International Affairs provided significant assistance.

    The government is represented by Assistant United States Attorneys Laura D. Withers and Stefanie A. Schwartz in these matters.

    It seems likely that FBI will go after the operator of Virtualine, and I'm looking forward in to the court documents. These allegations sound really serious.

  • edited October 27

    If you get accused, there is no way back. The letter isnt interesting for them.

  • edited 2:31AM

    AnonRDP.com next in line, may create a separate thread for it as its a separate can of worms. Their domain was already taken over by FBI, and they are attempting to move to anonrdp.st now. (archive)

    Domain Name: ANONRDP.COM
    Registry Domain ID: 2819374719_DOMAIN_COM-VRSN
    Updated Date: 2026-10-27T13:13:50Z
    Creation Date: 2023-10-04T23:25:09Z
    Registry Expiry Date: 2027-10-04T23:25:09Z
    Registrar: Tucows Domains Inc.
    Name Server: NS1.FBI.SEIZED.GOV
    Name Server: NS2.FBI.SEIZED.GOV

    LowEndSpirit - VPS Hosting and tech forum

    No seizure page yet. Their ASN is "Blatant Technologies, LLC" AS403005. Yet another bulletproof host, similar to Virtualine in terms of what is allowed.
    Their servers are located in Lithuania (with Serveroffer.lt/UAB Host Baltic AS209605 to be specific) and tunneled through SMARTNET (Aurologic competitor) in Germany.

    LowEndSpirit - VPS Hosting and tech forum

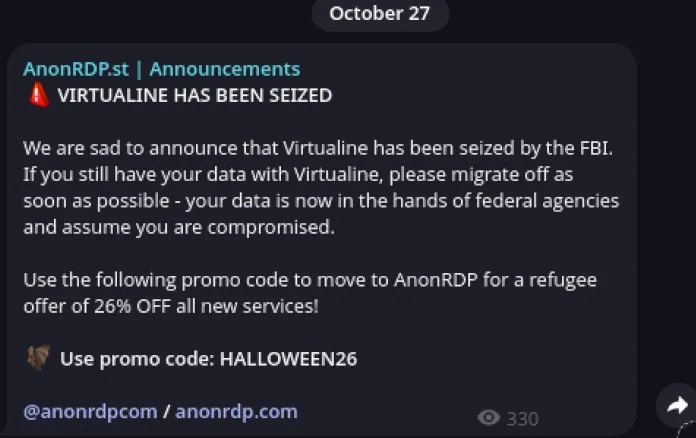
    Their marketing stunt from a few hours ago after Virtualine seizure, aged poorly. https://t.me/anonrdpcom/66 (archive)
    LowEndSpirit - VPS Hosting and tech forum

  • I was just getting spam from that Blatant Technologies ASN the other day and put the /24 in a blacklist.

Sign In or Register to comment.